
BE-CEC 2027 Q2
Belgium’s Cybersecurity Executives Conference
The afternoon where Belgium's IT and security leaders meet their peers.
Thursday June 10, 2027: 13:30 - 20:30
Dolce, La Hulpe
YOUR SECURITY IS ONLY AS STRONG AS YOUR WEAKEST SUPPLIER
YEARLY BBQ

YOUR SECURITY IS ONLY AS STRONG AS YOUR WEAKEST SUPPLIER
Cybersecurity does not stop at the boundaries of your organisation. Your suppliers, software providers, cloud platforms, technology partners and external service providers are all part of your attack surface. A vulnerability or security breach somewhere in this extended ecosystem can quickly become a serious threat to your own business.
As organisations become increasingly interconnected, managing third-party cyber risk is becoming one of the most challenging responsibilities for CIOs and CISOs.
-
How much do you really know about the security of your suppliers?
-
How can you assess and control risks beyond your own infrastructure?
-
And how do you build resilience when critical services depend on organisations and technologies outside your control?
At this edition of Belgium's Cybersecurity Executives Conference, we will explore how organisations can strengthen their security across the entire digital supply chain.
Join fellow CIOs, CISOs and IT leaders for an afternoon of thought-provoking presentations, practical insights and open discussions.
And because cybersecurity is also about building relationships and sharing experiences, we will finish the day with our traditional BE-CEC Summer BBQ at Dolce La Hulpe.
An afternoon of cybersecurity insights. An evening of networking, great food and a summer BBQ.
KEY TOPICS
-
The expanding attack surface: Understanding the cyber risks introduced by suppliers, partners and interconnected digital ecosystems.
-
Third-Party & Supply Chain Security: Moving beyond questionnaires and compliance towards continuous risk assessment and genuine security assurance.
-
Software Supply Chain & Product Security: Securing software dependencies, open-source components, connected products and the technology we rely on.
-
Digital Sovereignty & Cloud Dependencies: Understanding strategic dependencies and maintaining control over critical digital infrastructure.
-
From Compliance to Resilience: Turning NIS2, the Cyber Resilience Act and other regulatory requirements into practical security improvements.
-
Incident Response Across the Supply Chain: Are you prepared when a critical supplier gets hacked?
WHY ATTEND?
-
BE-CEC brings together Belgium's cybersecurity executives, CIOs, CISOs and IT decision-makers in an exclusive environment designed for knowledge sharing and peer-to-peer networking.
-
No exhibition stands, no product pitches and no unnecessary sales presentations. Just relevant content, experienced speakers and meaningful conversations with fellow IT leaders.
THE ANNUAL BE-CEC SUMMER BBQ
-
The June edition has become our annual summer gathering. After the conference programme, stay and enjoy an informal BBQ, drinks and networking in the beautiful surroundings of Dolce La Hulpe.
-
A great opportunity to reconnect with colleagues, exchange experiences and expand your professional network.
EVENT DETAILS
-
Date: Thursday, 10 June 2027
-
Time: 13:30 – 20:30
-
Location: Dolce La Hulpe, Chaussée de Bruxelles 135, 1310 La Hulpe, Belgium
-
Target audience: CIOs, CISOs, IT Directors, IT Managers and cybersecurity executives.
-
Participation: Free for selected IT decision-makers, subject to registration approval.
AGENDA
13:30 - 14:00 Registrations & Welcome Reception
14:00 - 14:30 Your Suppliers Are Your Attack Surface – And Hackers Know It
Your organisation's security is only as strong as the weakest link in its supply chain. Suppliers, subcontractors and technology partners increasingly have access to corporate systems, sensitive data and critical infrastructure. Cybercriminals understand these dependencies and actively exploit them to gain access to their ultimate targets. This session explores how supply-chain vulnerabilities are becoming a major attack vector and what organisations can do to identify, assess and reduce these risks.
14:30 - 15:00 The Cyber Resilience Act: Is Your Supply Chain Ready?
The European Cyber Resilience Act (CRA) introduces far-reaching cybersecurity requirements for products with digital elements, affecting manufacturers, software providers and organisations throughout the supply chain. Beyond regulatory compliance, it raises important questions about product security, vulnerability management, software updates and accountability. What does the CRA mean in practice for your organisation, your suppliers and your technology choices? And are businesses prepared for the changes ahead?
15:00 - 15:30 Break
15:30 - 16:00 Cyber Resilience Beyond Your Own Organisation
Cyber resilience cannot stop at the boundaries of your own IT environment. In an interconnected business ecosystem, an incident affecting a supplier, service provider or business partner can quickly become your own crisis. Building resilience therefore requires collaboration, shared responsibilities and a broader understanding of dependencies. This session examines how organisations can strengthen their collective resilience through better visibility, cooperation, risk management and incident preparedness across their extended business ecosystem.
16:00 - 16:30 Securing the Extended Enterprise: Lessons from a Critical Infrastructure Operator
Critical infrastructure operators face particular challenges when securing complex ecosystems involving suppliers, technology partners, operational systems and essential services. A security incident can have consequences far beyond the organisation itself. Drawing on the experience of a critical infrastructure operator, this session explores practical approaches to managing third-party risks, protecting interconnected IT and OT environments, and maintaining operational continuity in an increasingly hostile cyber landscape.
16:30 - 17:00 Break
17:00 - 17:50 The CISO Perspective
In this candid panel discussion, Pascal D'Eer, Chief Risk Officer (CRO) at the Belgian Federal Police, will interview experienced CISOs about their real-world experiences and key lessons learned in the field of cybersecurity. If you want to be inspired by how others do it and challenge the way of working in your own organisation, don't miss this opportunity.
Could your organisation continue operating if one of its strategic IT providers disappeared tomorrow?
17:50 - 18:00 Partner Spotlight
Our sponsors will briefly share who they are and how they support organisations in strengthening their cybersecurity posture.
18:00 - 20:30 Walking dinner
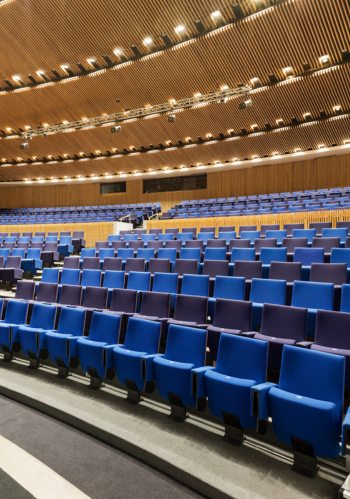
Dolce, La Hulpe
Dolce La Hulpe Brussels, nestled in the Sonian Forest, is a premier destination for business and leisure. Originally an IBM education center, it was transformed into a 4-star conference venue. Boasting 4,500 m² of state-of-the-art meeting space and cutting-edge technology, it ensures a seamless event experience. Guests can enjoy luxury at the Cinq Mondes Spa, a pool, fitness center, fine dining, and 264 elegant rooms. With comfort, professionalism, and tranquility, Dolce La Hulpe Brussels is the ideal setting for productive meetings, conferences, and seminars.
Chaussée de Bruxelles 135, 1310 La Hulpe
Sponsors



More events can be found on www.pointury.com